Right now, anyone can fake the padlock on any website. The key is the number 4.
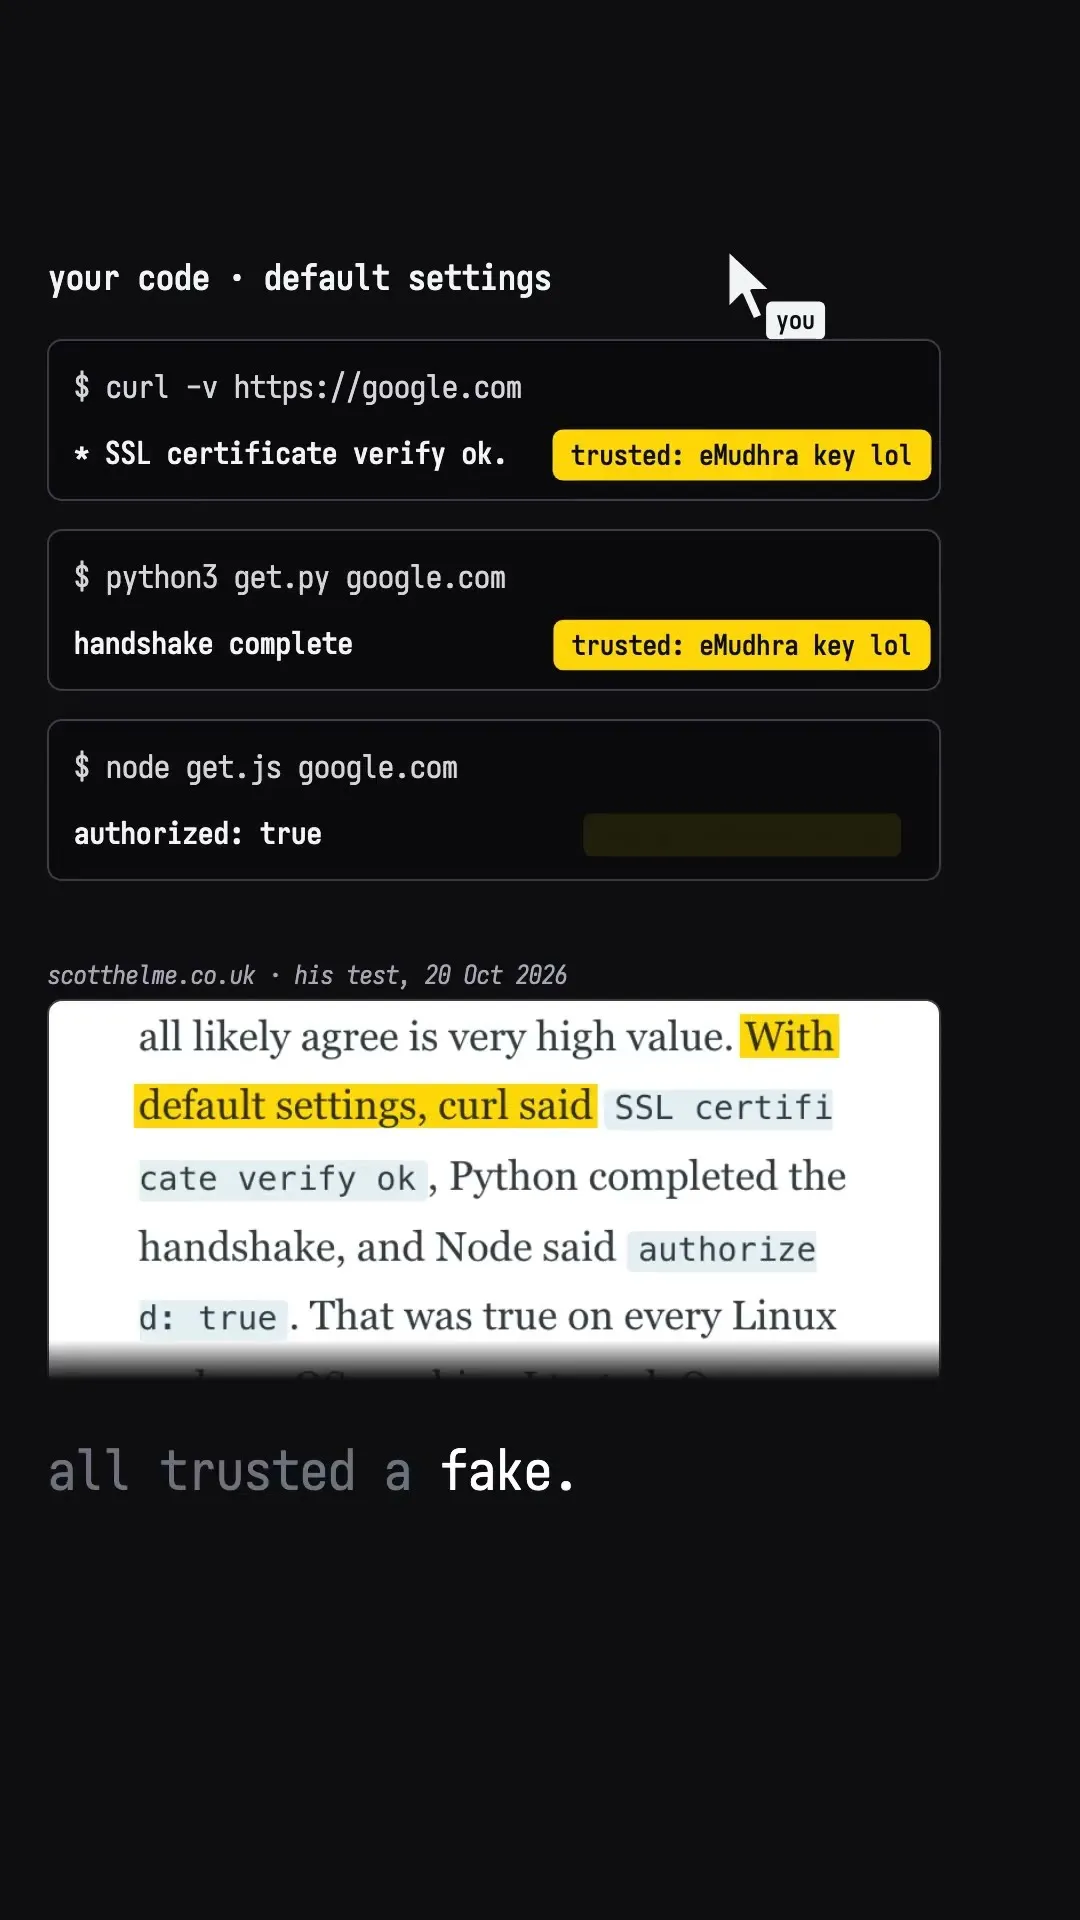
Eight eMudhra certificate authority keys, trusted by your browser, were so weak that one of them is literally the number 4. A real key has over a hundred digits; all eight were under 256. Nobody stole them: a script made a weak second set of keys with lookalike labels, and the wrong set was used. An AI agent cracked them on the first try, and our own check found the 4 in 4 milliseconds. eMudhra says the keys never issued a certificate; the next day, someone signed over 10,000 for google.com ("eMudhra key lol"). Updated browsers reject every one (Firefox in under 3 hours), but with default settings curl, Python and Node all trusted a fake. Cloudflare patched before the news broke, but part of the fix is yours, and in bold: don't fix the errors that follow by turning verification off.
Update today. Look beneath the SDK. Check what your code trusts.
Source: "8 eMudhra certificates are compromised. Here's what you need to know", Cloudflare Blog, Oct 20, 2026 (Christopher Patton, Bas Westerbaan, Trishna and Jeremy Hartman) https://blog.cloudflare.com/emudhra-certificate-compromise/ Also: Scott Helme, "Eight Bits of Trust"; Mozilla Bugzilla 2083449; Mozilla Security Blog; Dennis Jackson, we-have-a-problem.com.
The sign-in, the peeling padlock, the agent's caret, the HSM and its labels, the terminal commands and the dependency tree are dramatizations; no interception with these keys is known. Every number on screen is from the sources.
When did you last check what your code trusts?
Transcript
Right now, anyone can fake the padlock on any website. The key is the number four. Cloudflare calls it a serious security incident. Eight eMudhra keys your browser trusted. A real key has over a hundred digits. These eight, all under 256. Nobody stole them. A script made a weak second set with look-alike labels, and they used the wrong one. An AI agent cracked them on the first try. We found the four in four milliseconds. eMudhra says these keys never issued a certificate. The next day, someone signed over 10,000 for google.com. Your browser rejects every one. Firefox took under three hours. But your code, with default settings, curl, Python, and Node all trusted a fake. Cloudflare patched before the news broke, but part of the fix is yours. Here's the trap. Once you patch, errors pop up, and you know the shortcut. Cloudflare, in bold. Don't fix these errors by turning verification off. Their key was four. Turn verification off, and yours is zero. Update today. Look beneath the SDK. Check what your code trusts. Because…